· via Hacker News – Front Page (native)
Logic-only Microsoft Edge exploit chain earns $175,000 at Pwn2Own Berlin
A DEVCORE researcher chained logic flaws in Microsoft Edge's navigation handling into a full sandbox escape at Pwn2Own Berlin 2026, without a single memory-corruption bug.
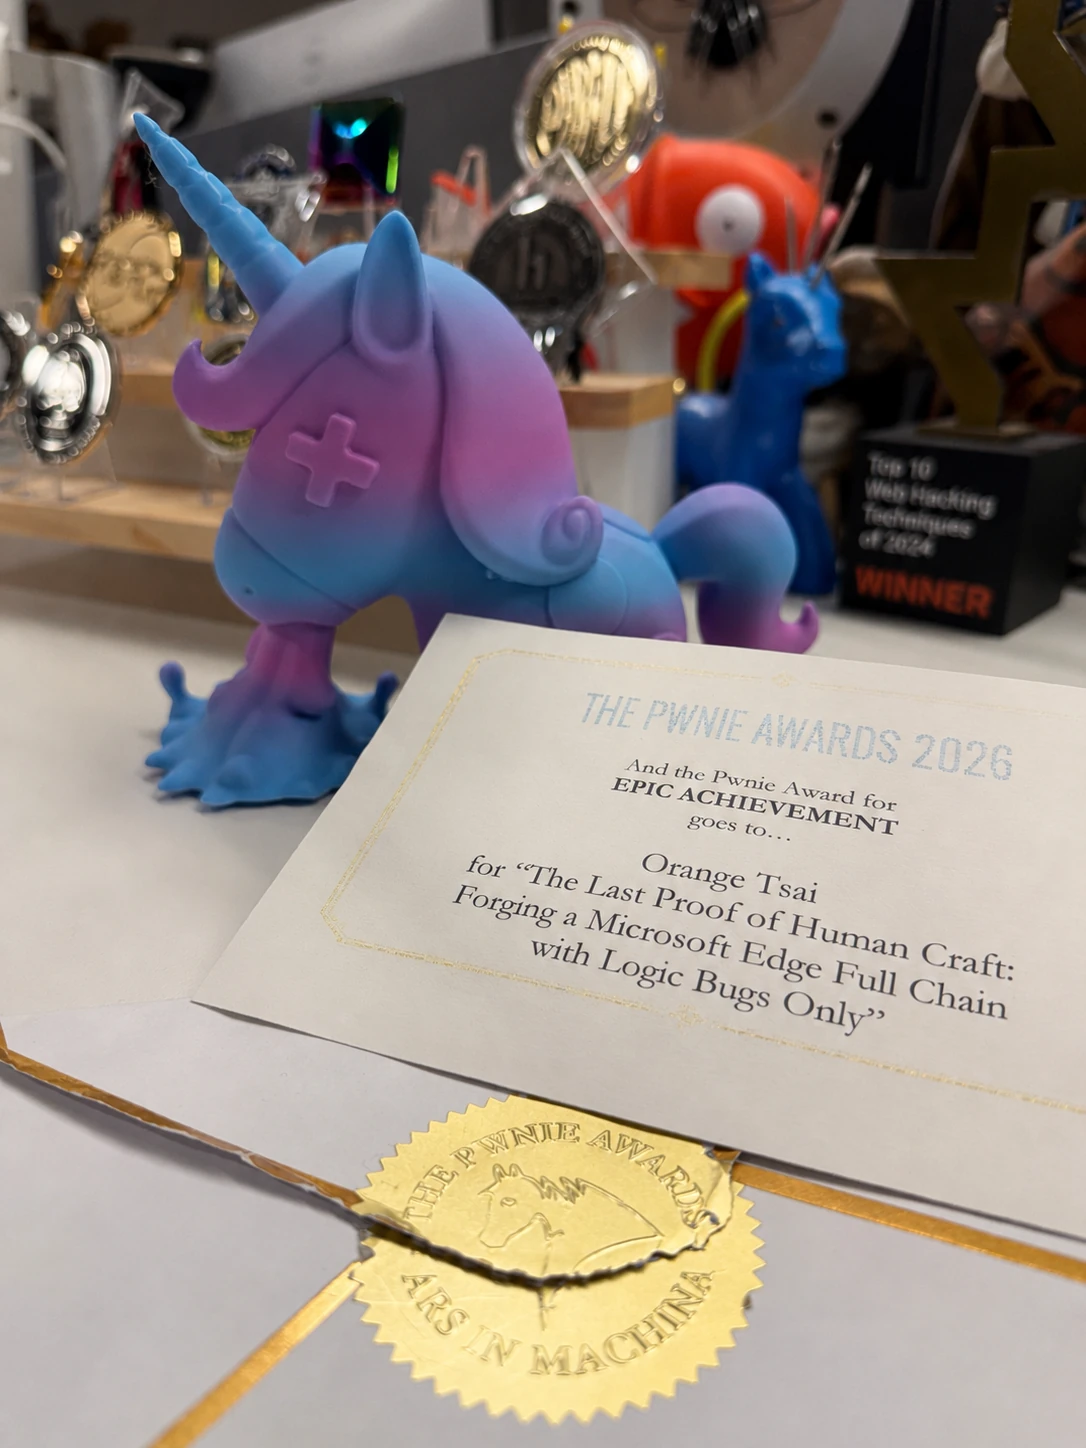
Security researcher Orange Tsai of the DEVCORE Research Team has published a full write-up of a Microsoft Edge exploit chain assembled purely from logic bugs and demonstrated at Pwn2Own Berlin 2026. According to the Zero Day Initiative, the contest entry achieved a sandbox escape in Edge and won $175,000 plus 17.5 Master of Pwn points. The two accounts differ slightly in scope: ZDI credited the winning demo to four chained logic bugs, while Tsai describes the complete project as five bugs combined with two Windows features.
No memory corruption, no AI
Most high-profile browser exploits hinge on memory-safety flaws. Tsai stresses that this chain involved no memory corruption at all, and he frames it as deliberately handmade work in an era when large language models are often assumed capable of finding everything. The work was later nominated at the Pwnie Awards, where it won the Epic Achievement prize, and he presented the bug-hunting and chaining process at the HITCON and Hexacon conferences.
An overlooked corner of Chromium
Tsai writes that the effort began with a study of how Chromium manages navigation, which drew him to navigation throttles — components in the browser process that intercept every navigation request, regardless of whether the browser or a renderer initiated it. He notes that of the more than 3,000 CVEs Google has patched in Chrome over the past five years, fewer than 20 relate to these throttles, making them a sparsely audited area. Comparing Chrome's and Edge's implementations, he identified an Edge-specific throttle, EdgeCAGuidanceNavigationThrottle, which supports the enterprise Conditional Access feature for Microsoft Entra ID by guiding users into the correct profile when they sign in with a work account on a Microsoft site.
How the throttle can be steered
The throttle fires only for navigations that begin on a Microsoft-owned origin such as login.live.com and use a special internal URL format carrying an email address and a switch_profile target. Edge compares the supplied email with the address on the current profile. If they differ, a dialog suggests switching profiles; if they match, Edge cancels the original navigation and launches a fresh one toward the URL supplied in switch_profile, using Chromium's internal navigation API. Because that second navigation originates in the browser process, it can reach destinations normally off-limits to web pages, including edge://settings, devtools:// URLs and even javascript: URIs. Tsai initially shelved the finding, judging it little more than a stronger open redirect that still executed script only in the login.live.com context.
The missing link back to the source tab
The breakthrough, he explains, came from asking which tab a browser-initiated navigation actually lands in. The page that triggers the throttle lives in a renderer, yet he found no code tying the new navigation back to it. A simple test settled the question: fire the throttled navigation after an eight-second delay, then switch to a different tab — for example google.com — during the wait. The navigation landed in whichever tab was active, producing script execution on google.com. The root cause sits in Chromium's Navigate() helper in browser_navigator.cc: when no source web contents are passed, it silently binds to the currently active tab, and the throttle's code path relies on exactly those defaults. Tsai points out that even Chromium's own sample code mishandles them, and he considers this pattern a new universal-XSS attack surface.
The zero-click hurdles
Turning the primitive into a practical, zero-interaction exploit posed further problems. Tsai lists four, the first being the trusted-origin requirement: the trigger must run on a supported Microsoft login page. Rather than hunt for a cross-site scripting flaw on such a site, which he calls a painful last resort, he examined Edge's origin check — which validates the last committed URL against supported login URLs — for a way around it, cracking the remaining obstacles with additional bugs.
Why it matters
A chain built only from logic flaws largely sidesteps the memory-safety hardening that has made traditional browser exploitation harder, showing that design and trust assumptions can be as decisive as memory corruption. It also illustrates how enterprise convenience features expand attack surface: a Conditional Access profile-guidance throttle in Edge became the entry point for a sandbox escape. For defenders and browser vendors, the post is a reminder that under-audited components such as navigation throttles — barely present in five years of Chrome CVE data — deserve closer scrutiny. And the Pwnie recognition underscores that patient, manual code reading still produces results that automated tooling has not.
- #microsoft-edge
- #security
- #exploits
- #chromium
- #pwn2own